


CISO Insights: Voices in Cybersecurity
CISO Marketplace
Supply Chain Hijacking; CI/CD Pipeline Defense
OCT 21, 202620 MIN
Description
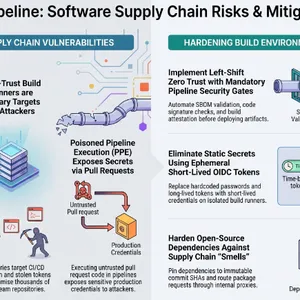
Modern enterprise software relies heavily on third-party dependencies, making developer pipelines and CI/CD workflows primary targets for supply chain attacks. Adversaries inject malicious code into open-source repositories, exploit unrotated API tokens in public cloud spaces, or manipulate build pipelines to compromise downstream targets. This episode outlines best practices for securing developer environments, enforcing automated dependency scanning, and managing secret rotation across automation platforms.
Week 3 Bonus Code: ' PASSKEYS '
Week three is open now, and the theme is identity and passkeys. The prize is a Nitrokey 3 plus $50 in CISO Marketplace credit. Your first submission adds 25 entries to the NitroPhone draw, and code PASSKEYS adds three more at https://cyberaware.win/c/PASSKEYS Entries close October 31st.
Buy Nitrokey direct: https://securitygadgets.shop/nitrokey
Enter free: https://cyberaware.win
Bonus entries (+25 for your first submission): https://cyberaware.win/community
No purchase necessary. Rules: https://cyberaware.win/rules
Full October schedule + all episodes: https://cisoinsights.show/security-awareness-2026/
#CyberAwareWin #CybersecurityAwarenessMonth