


The Identity Blueprint
Ernie Prescott
What Actually Breaks When You Migrate GPOs
SEP 29, 202641 MIN
Description
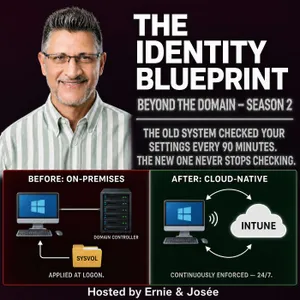
Ask to move one workload slider to Intune — just the Wi-Fi policy — and Microsoft silently drags your entire antivirus and BitLocker management along with it, whether you're ready or not. This episode is what actually breaks when you migrate off Group Policy, and why some of it isn't optional.
In this episode, Ernie and Josée trace why there's no cloud version of SYSVOL — the file share every Group Policy Object depends on — and why Microsoft never built one on purpose: the protocol itself can't survive being run across the public internet at global scale. We walk the actual mechanics of Intune's replacement architecture, the brutal translation gap that trips up admins moving legacy GPOs over (a hard 4-megabyte size limit, English-only text, and WMI filters that fail to translate at all), and the hidden dependencies buried inside co-management's workload sliders — including the one that silently forces three separate workloads to move together whether an admin intended that or not. We close with the exact endpoint logs administrators actually check to prove a transition worked, instead of trusting a cloud portal that can lag behind reality.
You'll leave knowing exactly what breaks first when you cut the cord to on-prem Active Directory, and the specific traps that catch even experienced admins off guard.
If you're the one planning a Group Policy migration, this episode is not optional.
Connect with Ernie Prescott on LinkedIn at linkedin.com/in/ernieprescott