
Ship It Weekly - DevOps, SRE, Platform and Cloud Engineering News
Teller's Tech - DevOps, SRE and Cloud Podcast
AWS Puts Elastic Beanstalk on EKS, CrowdSec Supply-Chain Breach, Critical Next.js RCE, Microsoft Disrupts EvilTokens & Why Fixing the Initial Compromise Isn’t Enough
SEP 25, 202617 MIN
Description
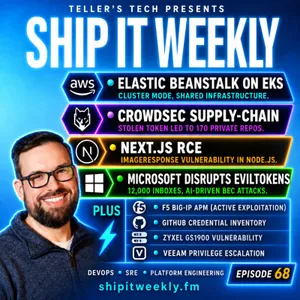
This week on Ship It Weekly: AWS introduced Elastic Beanstalk Cluster Mode, allowing multiple applications to run on shared EKS infrastructure while AWS handles much of the Kubernetes complexity. CrowdSec published how a software supply-chain compromise led to attackers copying roughly 170 private repositories using a stolen OAuth token. A critical Next.js vulnerability in ImageResponse can lead to remote code execution through attacker-controlled SVG data. And Microsoft disrupted EvilTokens, a cybercrime platform linked to more than 12,000 compromised inboxes across 10,000 organizations.
The bigger theme this week is what happens after trust has been established. Elastic Beanstalk Cluster Mode puts more infrastructure behind a managed abstraction, but shared infrastructure still means understanding isolation and blast radius. CrowdSec shows how an initial compromise can become a credential problem long after the malicious code is gone. Next.js shows how something as ordinary as generating a social preview image can expose a server-side execution path. And EvilTokens shows how attackers can use valid access to move faster once inside an account.
In the lightning round: F5 has a critical BIG-IP APM vulnerability under active exploitation. GitHub Enterprise Cloud can now export an inventory of credentials with enterprise access, including PATs, SSH keys, OAuth tokens, and GitHub App credentials. Zyxel patched a vulnerability affecting GS1900 switches. And Veeam Agent for Microsoft Windows has a privilege-escalation vulnerability that can lead to SYSTEM access.
And the human closer comes back to CrowdSec. Removing the malicious package, patching the server, or reimaging the workstation does not necessarily end the incident. If an attacker already stole an OAuth token, cloud credential, SSH key, session, or registry credential, that access can survive long after the original compromise is gone. Containment means understanding not only how the attacker got in, but what they took with them
Links
AWS Elastic Beanstalk Cluster Mode
https://tsn.io/1xaV7
CrowdSec Supply-Chain Attack Analysis
https://tsn.io/7yq2f
Next.js ImageResponse Security Advisory
https://tsn.io/8JvHp
Microsoft: Disrupting EvilTokens
https://tsn.io/DtbC9
Microsoft: EvilTokens and Device-Code Phishing
https://tsn.io/ZzwtD
F5 BIG-IP APM CVE-2026-94127
https://tsn.io/sFuKW
GitHub Enterprise Credential Inventory
https://tsn.io/7bpMn
Zyxel GS1900 Security Advisory
https://www.tellerstech.com/go/s-b2595852/
Veeam Agent for Microsoft Windows Vulnerability
https://www.tellerstech.com/go/s-166d3119/
This Week’s On Call Brief
https://tsn.io/Nnd8g
Ship It Weekly
https://tsn.io/NqkdP
On Call Brief
https://tsn.io/Gpz2d