
Ship It Weekly - DevOps, SRE, Platform and Cloud Engineering News
Teller's Tech - DevOps, SRE and Cloud Podcast
AWS Retires DevOps Guru: What the End of Support Means, Kubernetes Cross-Namespace CVE-2026-2270, Node.js Undici WebSocket DoS & Cloudflare’s New CLI for AI Agents
OCT 1, 202616 MIN
Description
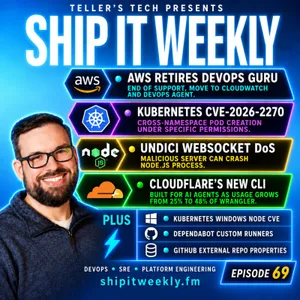
This week on Ship It Weekly: AWS is retiring Amazon DevOps Guru and pointing customers toward CloudWatch and the newer Amazon DevOps Agent. Kubernetes disclosed a vulnerability where StatefulSet and ControllerRevision permissions can allow cross-namespace pod creation under specific conditions. A vulnerability in Undici can let a malicious WebSocket server crash a Node.js process through compressed data. And Cloudflare launched a new CLI as AI agents grow from 25 percent to 48 percent of Wrangler usage.
The bigger theme this week is how the systems around our infrastructure are changing. Managed cloud services still have lifecycles that eventually become migration work. Kubernetes authorization can depend on what controllers do with the resources users are allowed to manipulate. Applications acting as clients still process untrusted data. And infrastructure tooling is starting to treat AI agents as first-class users rather than humans who happen to automate commands.
In the lightning round: another Kubernetes vulnerability affecting Windows nodes can expose NetNTLMv2 credentials through NTLM coercion. GitHub now supports custom runners for Dependabot version and security updates. And external systems like a CMDB or internal developer portal can push repository properties into GitHub while remaining the source of truth.
And the human closer comes from Lorin Hochstein and SRE Weekly. Some availability risks are probably never going away. Resources are finite, networks fail, security controls can affect availability, and production systems have to change. Preventing individual failures still matters, but incident response is part of reliability engineering too. Sometimes improving reliability means getting better at handling the failures you cannot eliminate.
Links
Amazon DevOps Guru End of Support - https://tsn.io/GQHN8
Kubernetes CVE-2026-2270: Cross-Namespace Pod Creation - https://tsn.io/BsNs8
Undici CVE-2026-85024: WebSocket Denial of Service - https://tsn.io/LncLd
Cloudflare: Introducing the cf CLI - https://tsn.io/Wk3ma
Cloudflare Forge - https://tsn.io/bAPJu
Lightning Round
Kubernetes CVE-2026-76654: Windows NTLM Coercion - https://tsn.io/36Kc3
GitHub: Custom Runners for Dependabot - https://tsn.io/tYl9K
GitHub: External Custom Properties - https://www.tellerstech.com/go/s-1fd1396d/
Human Closer
Omnipresent Availability Risks in Cloud Software - https://www.tellerstech.com/go/s-076db9dd/
Our Links
This Week’s On Call Brief - https://tsn.io/fKB9V
Ship It Weekly - https://tsn.io/NqkdP
On Call Brief - https://tsn.io/Gpz2d