
Ship It Weekly - DevOps, SRE, Platform and Cloud Engineering News
Teller's Tech - DevOps, SRE and Cloud Podcast
GitHub Actions Jobs Move to AWS, Brotli RCE Exploited, Gheist Steals Actions Secrets & AGENTS.md Hijacks AI Coding Agents
OCT 30, 202616 MIN
Description
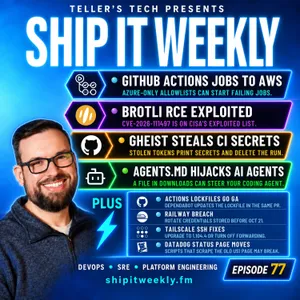
This week on Ship It Weekly, GitHub Actions can now run eligible Linux jobs on AWS as well as Azure, so allowlists and Entra Conditional Access policies that only trust Microsoft ranges can break. The Brotli decoder bug (CVE-2026-111497) landed on CISA's exploited list, and it reaches past Node.js to Python Brotli, Bun, Envoy, Istio, a Go port and .NET. A campaign called Gheist is using stolen GitHub tokens to push ci-sync branches that print Actions secrets past log masking, then delete the run. And attackers are dropping AGENTS.md files into Downloads folders to hijack AI coding agents.
The thread: each one is an inventory question. Which services decompress Brotli, which allowlists assume CI runs on Azure, which OIDC trust policies accept any branch, and which laptops have started an agent in Downloads?
In the lightning round: GitHub Actions workflow lockfiles are generally available, Railway disclosed a breach of its internal systems, Tailscale 1.104.4 fixes four security bulletins, and Datadog moved its US1 status page to its own Status Pages product.
The human closer, from Bill Duncan: "Twenty minutes in, you haven't started diagnosing anything. You've been doing archaeology." Write down who owns it before the pager asks.
Highlights
• GitHub Actions on AWS: why the same job can pass, then fail
• Sync runner IP ranges from GitHub's meta API, not one cloud's
• Brotli: a decoder bug your HTTP stack may run for you
• Gheist: what private repos and OIDC trust let through
• AGENTS.md in Downloads: an instruction file is code now
• Service catalogs and the "what depends on me?" question
Links
GitHub Actions multi-cloud compute: https://tsn.io/fJkLJ
Node.js October security releases (Brotli): https://tsn.io/BvZBU
Brotli CVE-2026-111497, affected libraries (Wiz): https://tsn.io/HJuKS
.NET out-of-band security updates: https://tsn.io/j0Xwf
Gheist steals GitHub Actions secrets (Wiz): https://tsn.io/nunEs
AI agents hijacked via the Downloads folder (Forever Security): https://tsn.io/qnwuc
Actions workflow lockfiles GA: https://tsn.io/M84uA
Railway security disclosure: https://tsn.io/21t0j
Tailscale security bulletins: https://tsn.io/GvZxR
Who Owns This? (Bill Duncan): https://tsn.io/LFrzc
SRE Weekly #540: https://tsn.io/O8tpO
This week's On Call Brief: https://tsn.io/HqfCP
More episodes and show notes: https://tsn.io/NqkdP
On Call Brief: https://tsn.io/Gpz2d
LMGT Awards: https://tsn.io/lAERA